
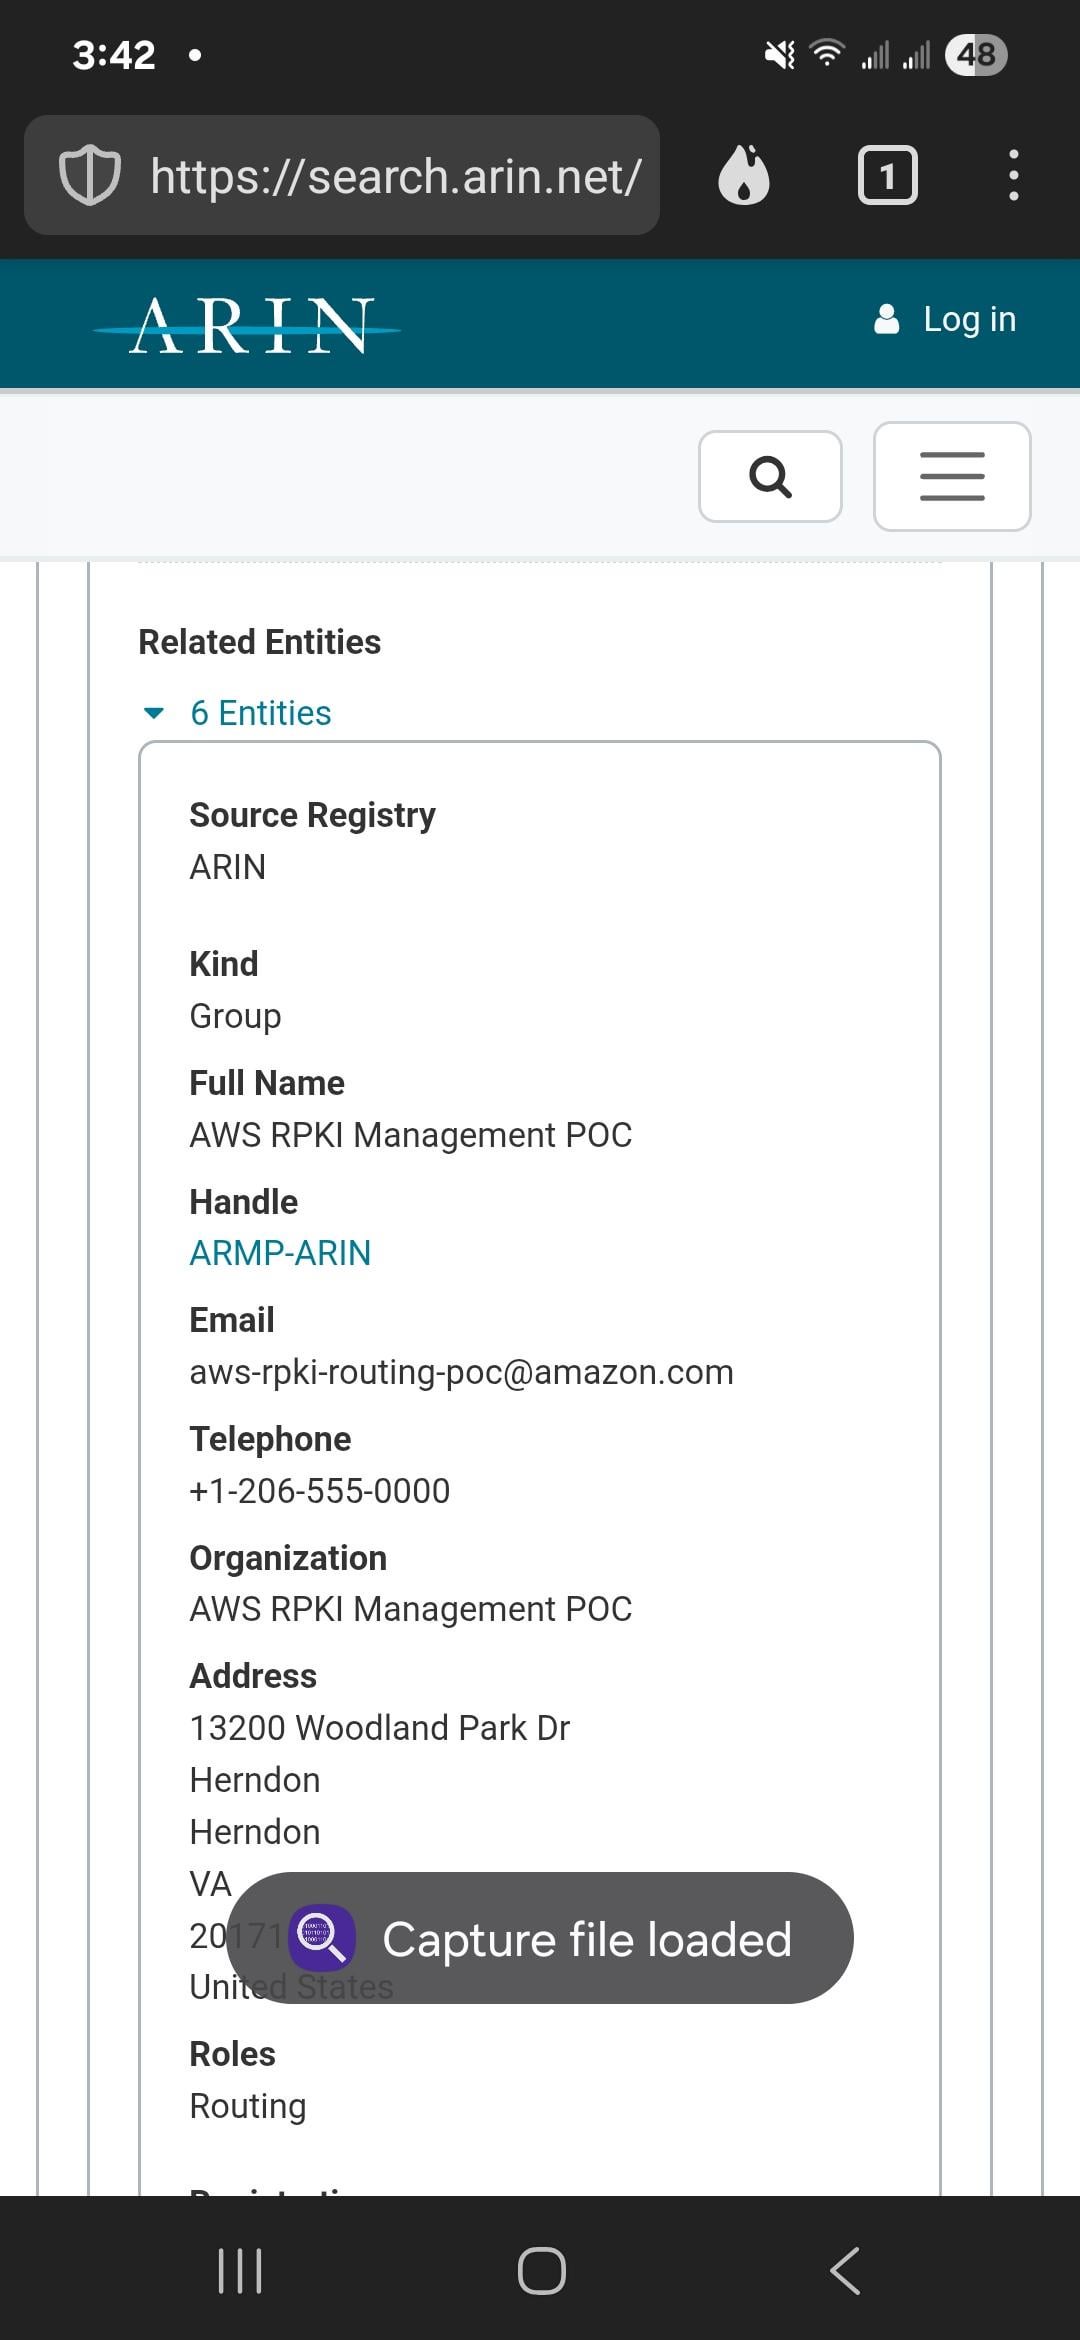
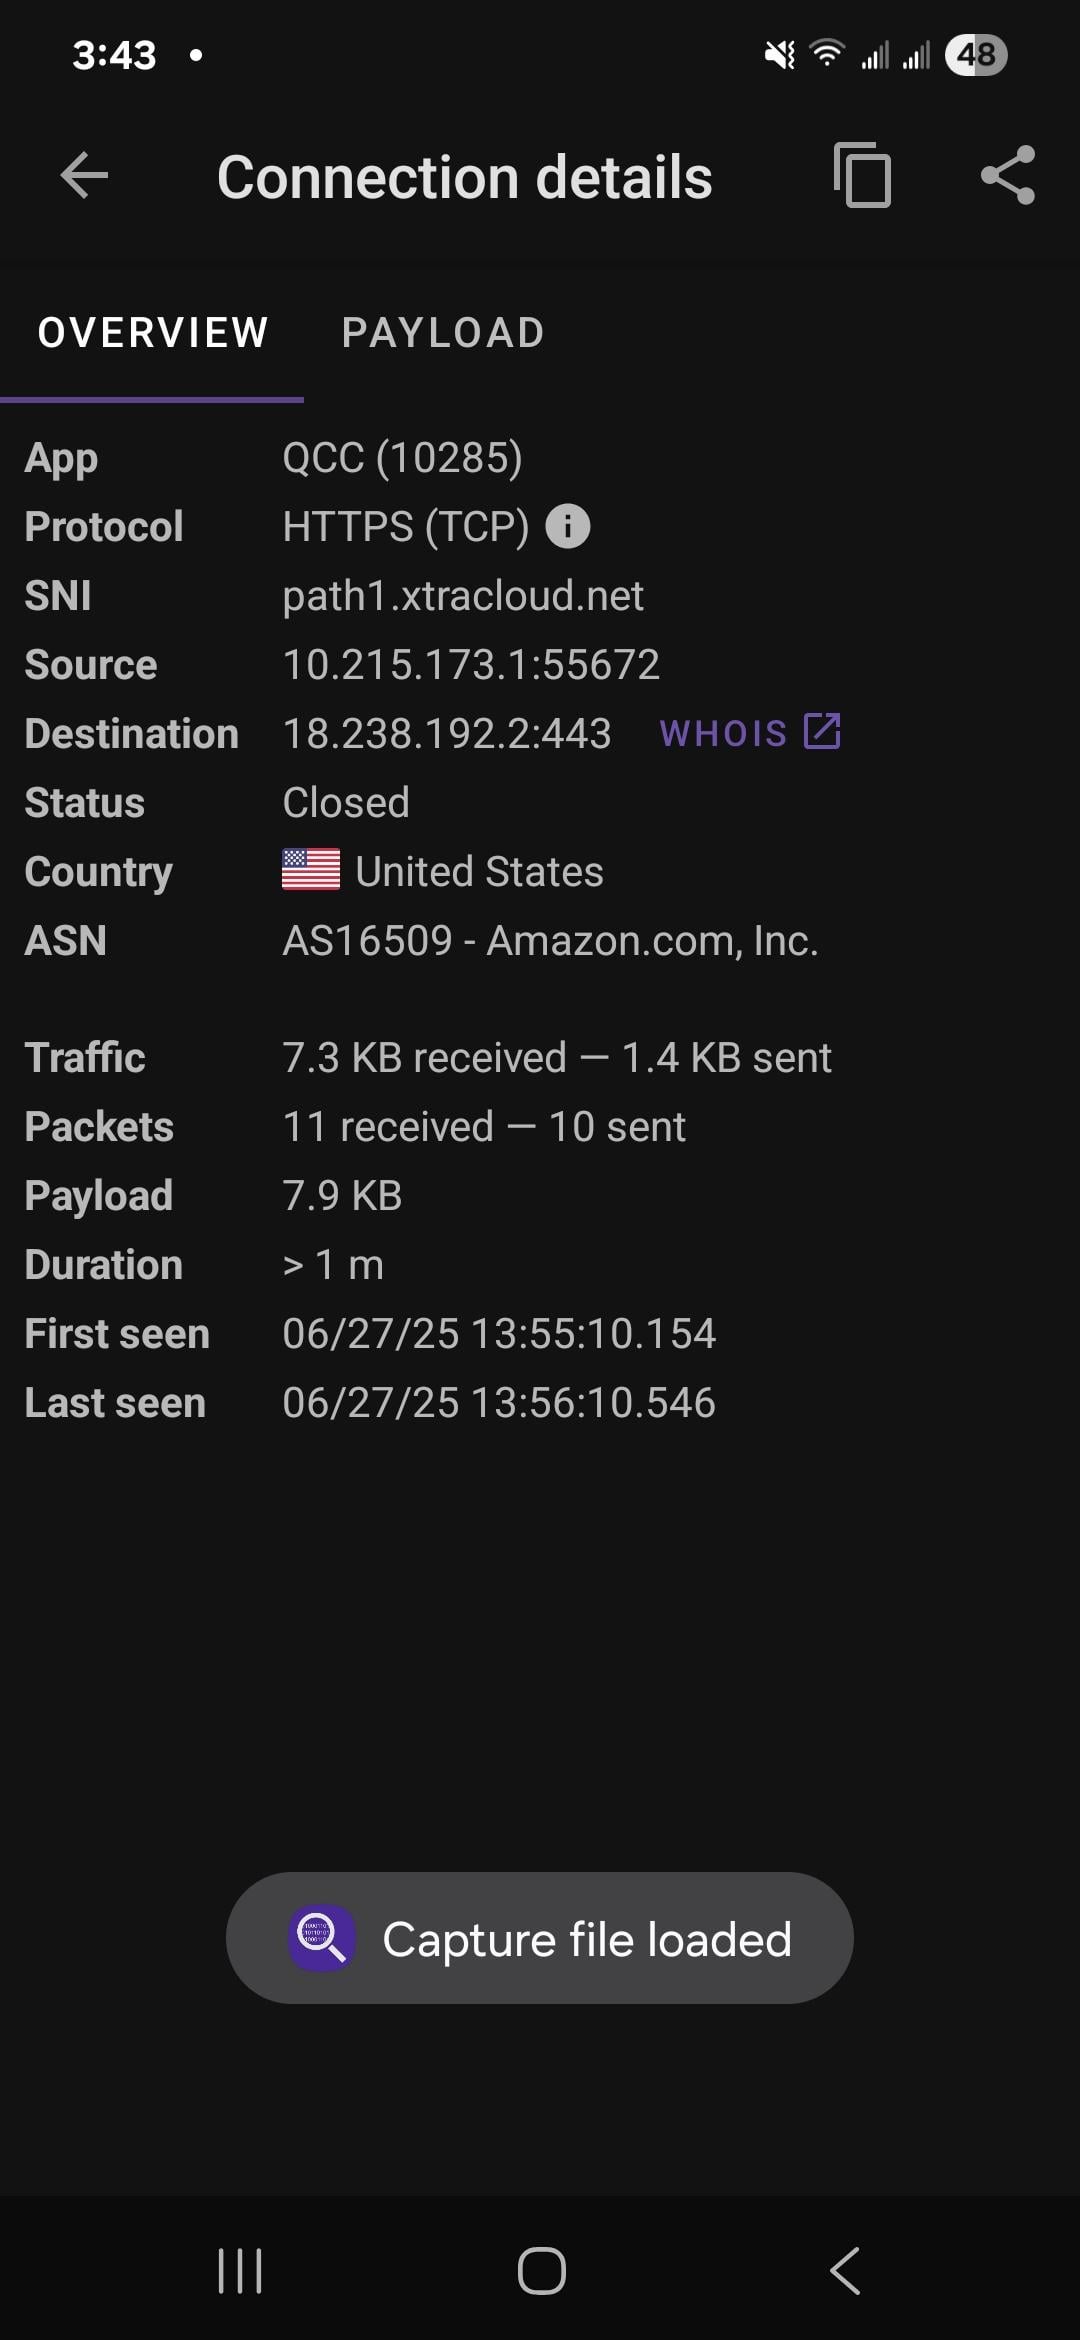
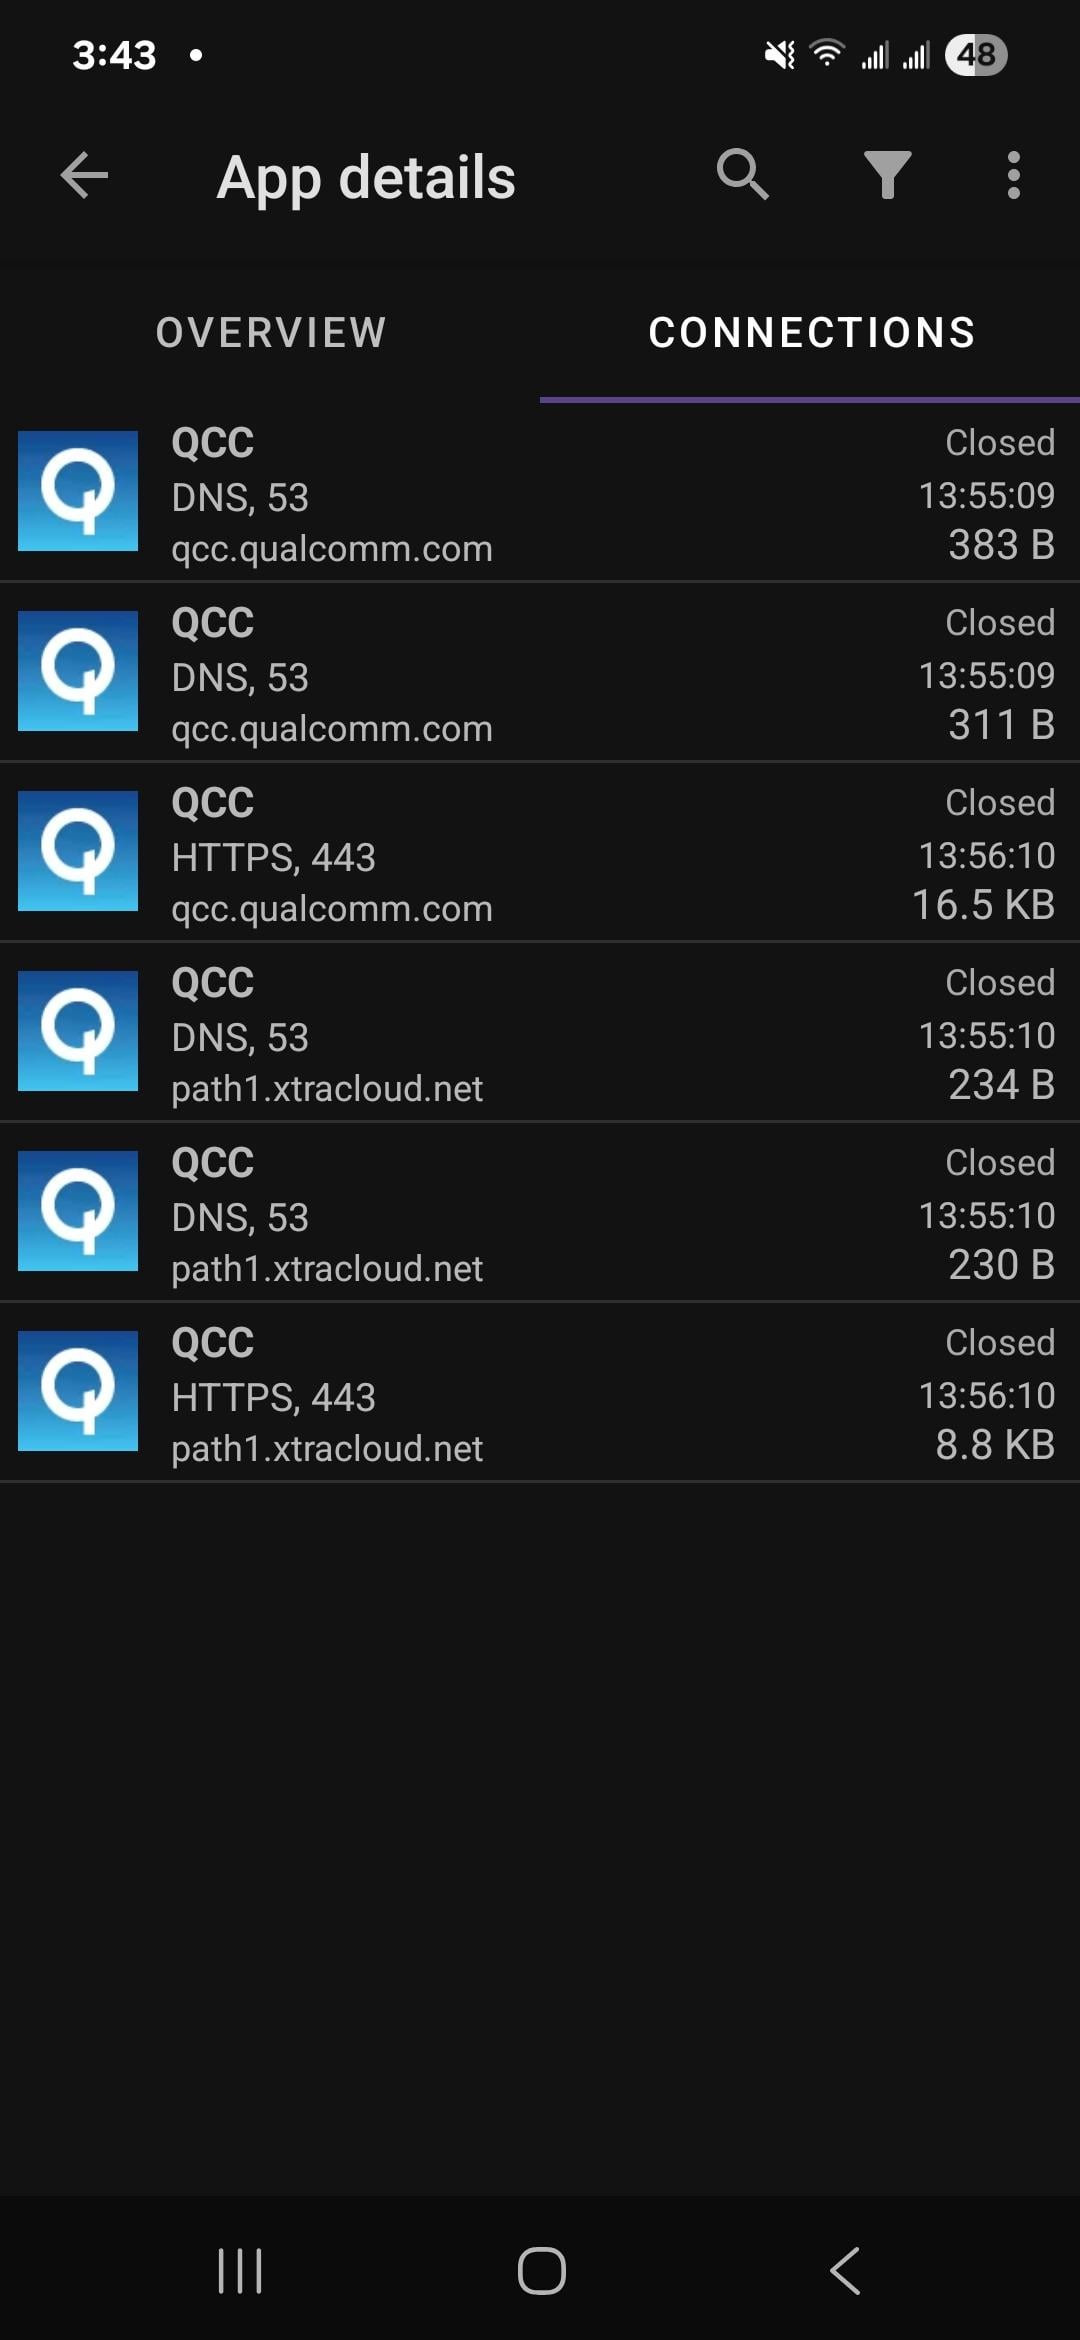
There's the screenshots as requested.
On June 27 2025 I captured a live outbound encrypted connection from a mobile app installed on my personal device. The app called QCC initiated the connection silently. No user action. No notification. No permission request. Just a raw encrypted handshake to an Amazon AWS EC2 server
Here is the forensic breakdown of the session
App QCC UID 10285
Protocol HTTPS TCP
SNI path1.xtracloud.net
Source IP 10.215.173.1 port 55672
Destination IP 18.238.192.2 port 443
ASN AS16509 Amazon.com Inc
Payload size 1.4 KB sent and 7.3 KB received
Packets 10 up and 10 down
Duration 237 milliseconds
Decryption status Fully encrypted TLS
Region United States
Registry ARIN
WHOIS confirmed the routing passed through Amazon AWS EC2 cloud infrastructure. These are not random IPs. These are tied to official AWS registration points and abuse handling contacts. This includes
ARMP ARIN AWS RPKI routing management
IPROU3 ARIN AWS IP routing infrastructure
AEA8 ARIN Amazon EC2 abuse contact
The domain path1.xtracloud.net is a masked backend endpoint. It is not mentioned in any privacy policy. It is not user facing. It is not tied to any in-app function. It runs silently without disclosure
This was not a user update. Not content retrieval. Not scheduled sync. This was a silent telemetry ping or instruction pull that triggered while the app was idle. The response payload was significantly larger than the request which suggests data or command receipt
I have submitted a report to AWS and formally requested legal-only communication for resolution. I will not be responding to engineering staff or abuse desk inquiries. All logs have been preserved including DNS traces timestamps SNI records and process origin IDs. Everything is backed up in cold storage and ready for legal review
This activity violates multiple regulatory frameworks and federal protections
California Consumer Privacy Act
No disclosure of data flow
No opt-out control
No permission granted
General Data Protection Regulation
Violation of transparency and purpose limitation
No identification of data controller
No lawful basis for processing
Federal Trade Commission Act Section 5
Unfair and deceptive practices
Hidden data transfer to third party routing
Electronic Communications Privacy Act
Unauthorized transmission over secured electronic systems
Concealment of intent through TLS and EC2 relay
Computer Fraud and Abuse Act
Unapproved system behavior initiated outside of scope
Execution of non-permissioned background activity on a user device
This is the kind of backchannel behavior most people will never catch unless they are running full packet logging or DNS level firewalls. I caught it. I am exposing it. I will continue publishing if this goes ignored
If you run QCC or any related apps I suggest checking your outbound connections. Tools like PCAPdroid RethinkDNS and NetGuard can confirm if your device is doing the same
Posted by NWRacer88
1 Comment
https://gitlab.com/CalyxOS/calyxos/-/issues/370
It’s related to the Qualcomm GPS. If you want your phone GPS to stay accurate, you’ll want it communicating.